11月5日,国家重点研发计划“网络空间安全治理”重点专项“非受控环境下数据资产保护关键技术研究”项目综合绩效评价会在国科大玉泉路校区召开。
项目管理专业机构领导、国科大科研处副处长刘彦、评审专家、项目承担单位代表和各课题负责人、第三方测试机构和用户代表等参加会议。
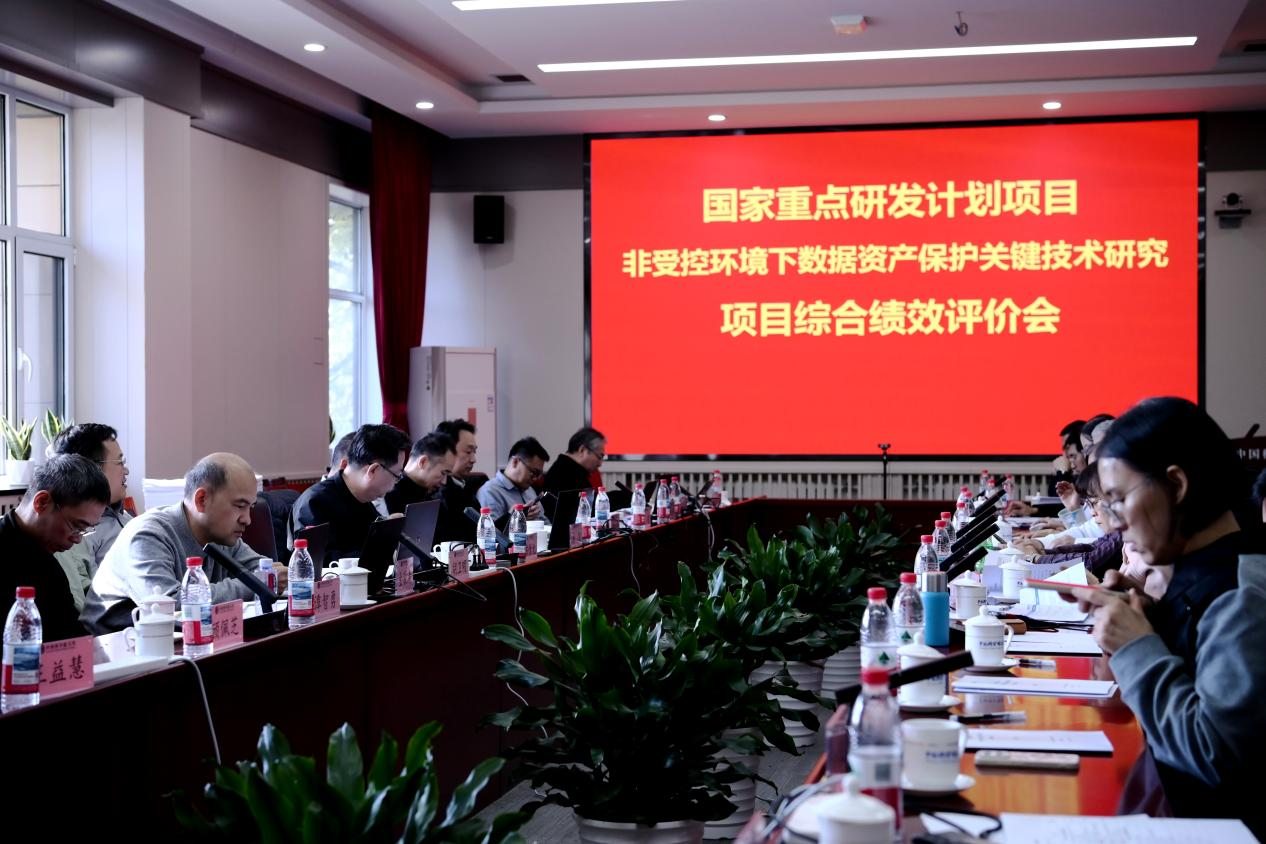
项目综合绩效评价会现场
项目负责人、国科大密码学院院长荆继武教授汇报了项目实施情况、主要成果及应用示范情况。专家组听取汇报,抽测了项目主要任务目标和核心指标,对项目资料和财务资料进行审查,结合成果演示和现场质询开展评议。
该项目由中国科学院大学牵头,联合高校、科研院所和企业共同开展研究,围绕非受控环境下终端、网络和云端的数据安全保护,开展关键技术攻关、安全检测评估及应用示范,形成了多款产品、原型系统和工具平台。
2026年10月23日下午,中国科学院大学密码学院第一届研究生会成立大会顺利举行。学院学生主管胡佳、2026级新生班主任黄娜娜参会,大会依次完成主席团竞选发言、学生不记名投票及各部门负责人评选等议程。
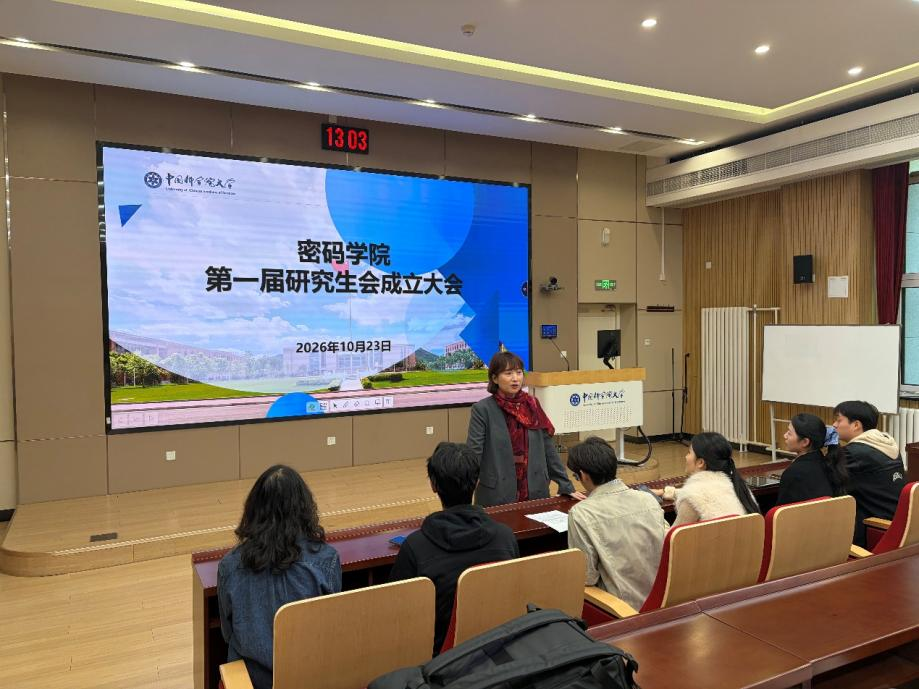
会议照片
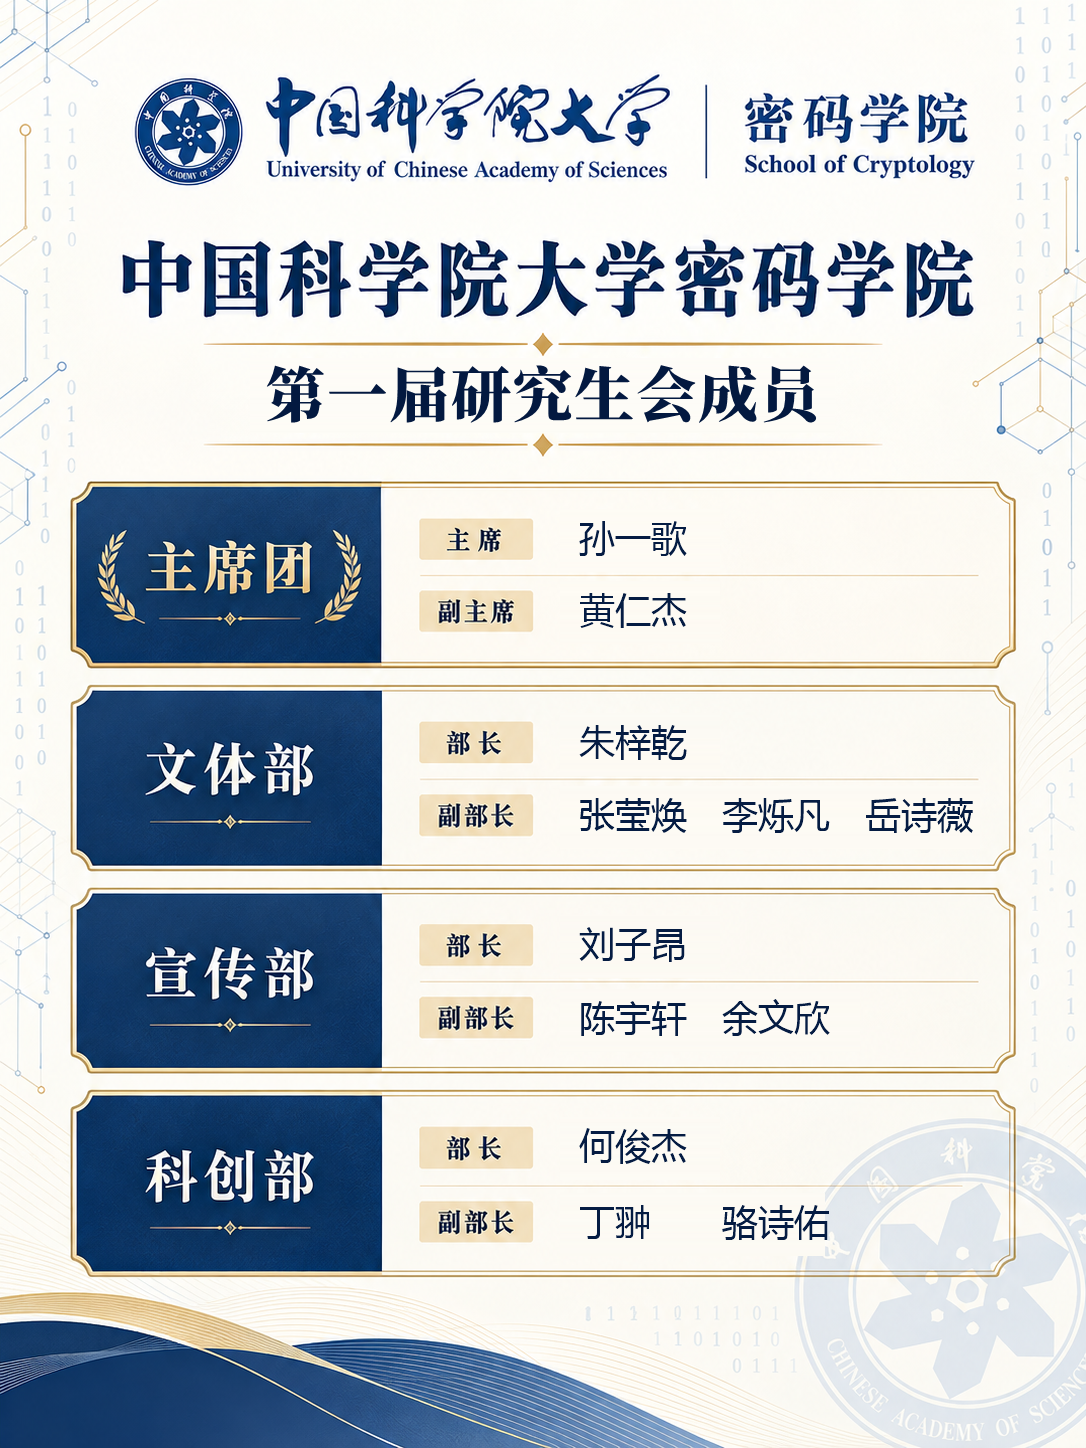
共计五位同学先后上台发表研究生会主席团竞选讲话。同学们结合自身相关学生工作经历,围绕服务意识、组织协调与团队建设等方面阐述工作设想。经现场不记名投票,孙一歌同学、黄仁杰同学分别以最高票和次高票当选密码学院第一届研究生会主席与副主席。
孙一歌同学表示,第一届研究生会肩负开局起步、建章立制任务,主席团应定位为“服务者、协调者与推动者”,向上对接校院任务、反馈同学诉求,向下统筹部门协作。黄仁杰同学则结合自己学生会体育部及生活文化部等组织工作经历,提出研究生会应成为同学们遇到困难愿意求助、提出建议能够得到回应的地方。
在主席团正式确立以后,主席和副主席共同完成了本届研究生会各部门部长及副部长评选工作。
近日,中国科学院大学(国科大)密码学院在国际密码学顶级会议CRYPTO 2026上同时发表两篇研究论文,分别聚焦于杂凑函数的新型结构设计和低轮Feistel类密码的安全性分析,两项成果均具有重要理论价值和实际应用前景。
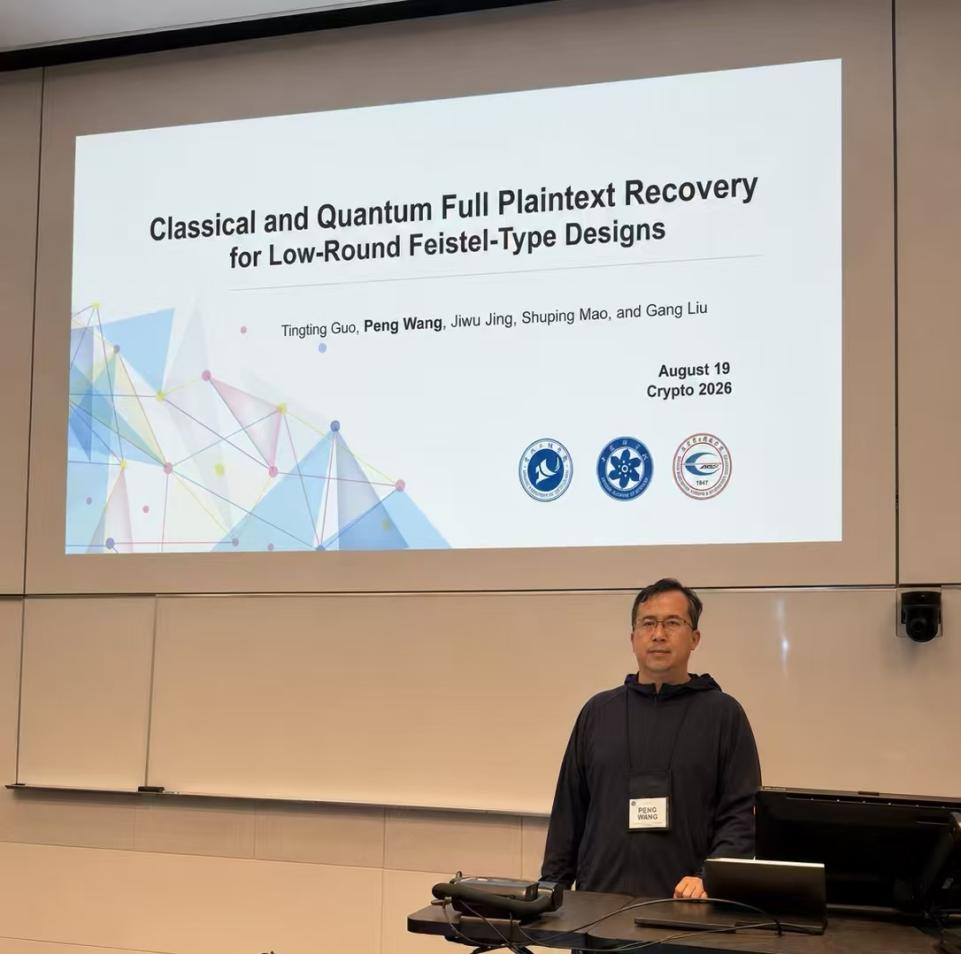
王鹏参会照片
CRYPTO(International Cryptology Conference,又称“美密会”)由国际密码研究协会(IACR)主办,与欧密会、亚密会并列为全球密码学领域三大旗舰会议,代表着密码学理论研究的最高水准。本届会议于2026年8月17日至20日在美国加州大学圣巴巴拉分校举行,共收到创纪录的781篇投稿,最终录用193篇论文,录用率约24.7%。国科大密码学院王鹏副教授赴美参会,并就相关研究成果作了学术报告。
论文一:突破Sponge结构原像安全性瓶颈的新型杂凑设计
第一篇论文题为《Permutation-Based Hashing With Stronger (Second) Preimage Resistance》(基于置换的具有更强(第二)原像抗性的杂凑设计),作者为孙思维教授,李顺特别研究助理,张志宇特别研究助理,法国雷恩大学博士后研究员Charlotte Lefevre,荷兰马斯特里赫特大学Bart Mennink教授,秦臻博士生以及冯登国院士。
经典Sponge杂凑结构的原像与第二原像安全性长期受限于容量参数(capacity),成为制约其高安全等级应用的关键瓶颈。该研究创造性地在吸收阶段引入Davies–Meyer型前馈机制,使置换操作不再保持传统可逆性,从而切断了已有攻击依赖的关键路径。新提出的SPONGE-DM和SPONGE-EDM系列结构,在保持与标准Sponge相同碰撞安全水平的前提下,将原像安全性提升至完整的n比特,并显著增强第二原像安全边界。更为重要的是,该改进无需增加底层置换的调用次数,仅需额外进行异或和状态保存操作,工程实现成本极低。
论文以Keccak和Ascon置换为例给出了具体实现:使用800比特的Keccak即可达到512比特的原像与第二原像安全强度,而标准1600比特的Keccak可实现1024比特的超高安全等级,完全满足我国新一代商用密码杂凑算法对极高安全性的需求。此外,该方法还能有效提升基于杂凑的后量子签名方案的安全性与效率,为高安全等级杂凑函数设计提供了一条兼顾理论强度与实现可行性的新路径。
论文二:揭示低轮Feistel“可区分”即“可解密”的内在关联
第二篇论文题为《Classical and Quantum Full Plaintext Recovery for Low-Round Feistel-Type Designs》(低轮Feistel类结构的经典与量子完整明文恢复攻击),通讯作者为王鹏副教授。
该工作重新审视了低轮Feistel结构的安全边界,揭示出一个远比传统“区分攻击”更严重的隐患:几乎所有能够区分Feistel结构与随机置换的攻击,都可以在查询复杂度基本不变的前提下,直接升级为完整明文恢复攻击。经典模型下,论文证明针对2轮Feistel的选择明文攻击和3轮Feistel的选择密文攻击,仅需3次查询即可恢复任意目标密文的全部明文。量子模型下,借助Simon算法设计的前向与后向轮扩展技术,攻击可推进至3轮Feistel的量子选择明文攻击和4轮Feistel的量子选择密文攻击,量子查询复杂度仅为O(n)。
该攻击的普适性尤为突出——其核心依赖于Feistel的两分支结构本身,而非具体轮函数,因此可推广至UFLM、Lai–Massey、Feistel-FK等类Feistel结构,并进一步适用于AEZ-core、FMix、OleF、double-decker等实际加密方案。这一成果首次系统建立了低轮Feistel中“区分性”与“解密性”之间的结构性联系,将安全分析从识别非随机性推进到恢复全部明文,为经典和量子环境下Feistel类设计的轮数选择与安全评估提供了全新警示和理论依据。
两项成果的集中发表,展示了国科大密码学院在对称密码基础理论与前沿安全分析领域的持续创新能力和国际学术影响力,也为我国自主密码算法的设计分析与标准化提供了重要技术支撑。
Abstract:The sponge is a popular construction of hash function design. It operates with a $b$-bit permutation on a $b$-bit state, that is split into a $c$-bit inner part and an $r$-bit outer part. However, the security bounds of the sponge are most often dominated by the capacity $c$: if the length of the digest is $n$ bits, the construction tightly achieves $\min\{n/2,c/2\}$-bit collision resistance, $\min\{n,c/2\}$-bit second preimage resistance, and $\min\{n,\max\{n-r,c/2\}\}$-bit preimage resistance. Here, it is noteworthy that the generic attacks matching the preimage and second preimage bounds make use of the inverse of the permutation. We demonstrate that, by a relatively simple adjustment, significantly improved preimage and second preimage resistance can be achieved. In detail, we first present the SPONGE-DM construction, that differs from the sponge by evaluating the permutation during absorption in a Davies-Meyer mode. This construction generically achieves $\min\{n/2,c/2\}$-bit collision resistance as the sponge does, but $n$-bit preimage resistance and $\min\{n,c-\log_2(\alpha)\}$-bit second preimage resistance, where $\alpha$ is the maximum size of the first preimage in blocks. Next, we investigate how improved security can be achieved with a smaller feed-forward, and we present the SPONGE-EDM$^a$ family of functions, indexed by a parameter $a\in\{0,\ldots,b\}$. These functions replace the permutation during absorption in the sponge by an Encrypted Davies-Meyer mode, but with only $a$ bits of feed-forward. For $a=b$, comparable bounds as for SPONGE-DM are obtained, and these bounds gradually decrease to the original sponge bounds for decreasing values of $a$. We present various instantiations of SPONGE-DM and SPONGE-EDM$^a$ using the Keccak and Ascon permutations, and concretely demonstrate the immediate security and performance gains of these instances. For example, one can achieve up to $512$-bit preimage and second preimage resistance using the $800$-bit Keccak permutation (rather than 1600-bit in SHA-3), and likewise, one can use the $1600$-bit Keccak permutation to easily achieve up to $1024$-bit preimage and second preimage resistance (therewith properly fitting within the recently announced Chinese call for a new generation of cryptographic algorithms). Finally, we show the benefits of using these instantiations in the context of hash-based signature schemes whose security relies solely on the (second) preimage resistance of the underlying hash functions (such as Ascon-Sign).
论文信息:Siwei Sun. Shun Li. Zhiyu Zhang. Charlotte Lefevre. Bart Mennink. Zhen Qin. Dengguo Feng: “Permutation-Based Hashing With Stronger (Second) Preimage Resistance" ” in the 46th Annual International Cryptology Conference (CRYPTO 2026)(CCF-A)
Abstract:The Feistel (Luby-Rackoff) structure underlies numerous block-cipher and mode-of-operation designs, whose security is traditionally assessed via indistinguishability. For low-round Feistel constructions, a variety of classical and quantum distinguishing attacks are known. In this work, we show that such distinguishing attacks can be systematically upgraded to full plaintext recovery with essentially the same query complexity. We establish classical recovery attacks on the 2-round Feistel under CPA and the 3-round Feistel under CCA using only three queries, and introduce quantum-assisted forward/backward extension techniques based on Simon’s algorithm that yield recovery attacks on the 3-round Feistel under qCPA and the 4-round Feistel under qCCA. We further prove that the attacks extend to the Unified Feistel-Lai-Massey (UFLM) framework and therefore apply to a broad class of two-branch constructions. As a consequence, we obtain plaintext-recovery attacks on 4/5/6-round Feistel-FK and on several practical enciphering schemes, including AEZ-core, FMix, OleF, double-decker, and docked-double-decker. Overall, our results reveal a fundamental connection between distinguishing and full plaintext recovery in low-round two-branch Feistel-type designs, in both classical and quantum settings.
论文信息:Tingting Guo. Peng Wang. Jiwu jing. Shuping Mao. Gang Liu: “Classical and Quantum Full Plaintext Recovery for Low-Round Feistel-Type Designs” in the 46th Annual International Cryptology Conference (CRYPTO 2026)(CCF-A)
2026年9月7日,国科大密码学院2026年开学第一课暨新生导师见面会于玉泉路校区顺利举行。
“密码学院第一课”由学院名誉院长冯登国院士主讲。冯登国院士从行业背景概述、密码领域发展历程及主要工作、密码学科知识体系思考这三个维度展开授课。立足我国密码事业发展现实背景,系统梳理密码领域的发展脉络与工作实践,带领全院师生厘清密码学科的发展逻辑、学科定位与知识框架,帮助同学们建立起对密码学科的全貌、研究范畴与发展方向系统性的认知。
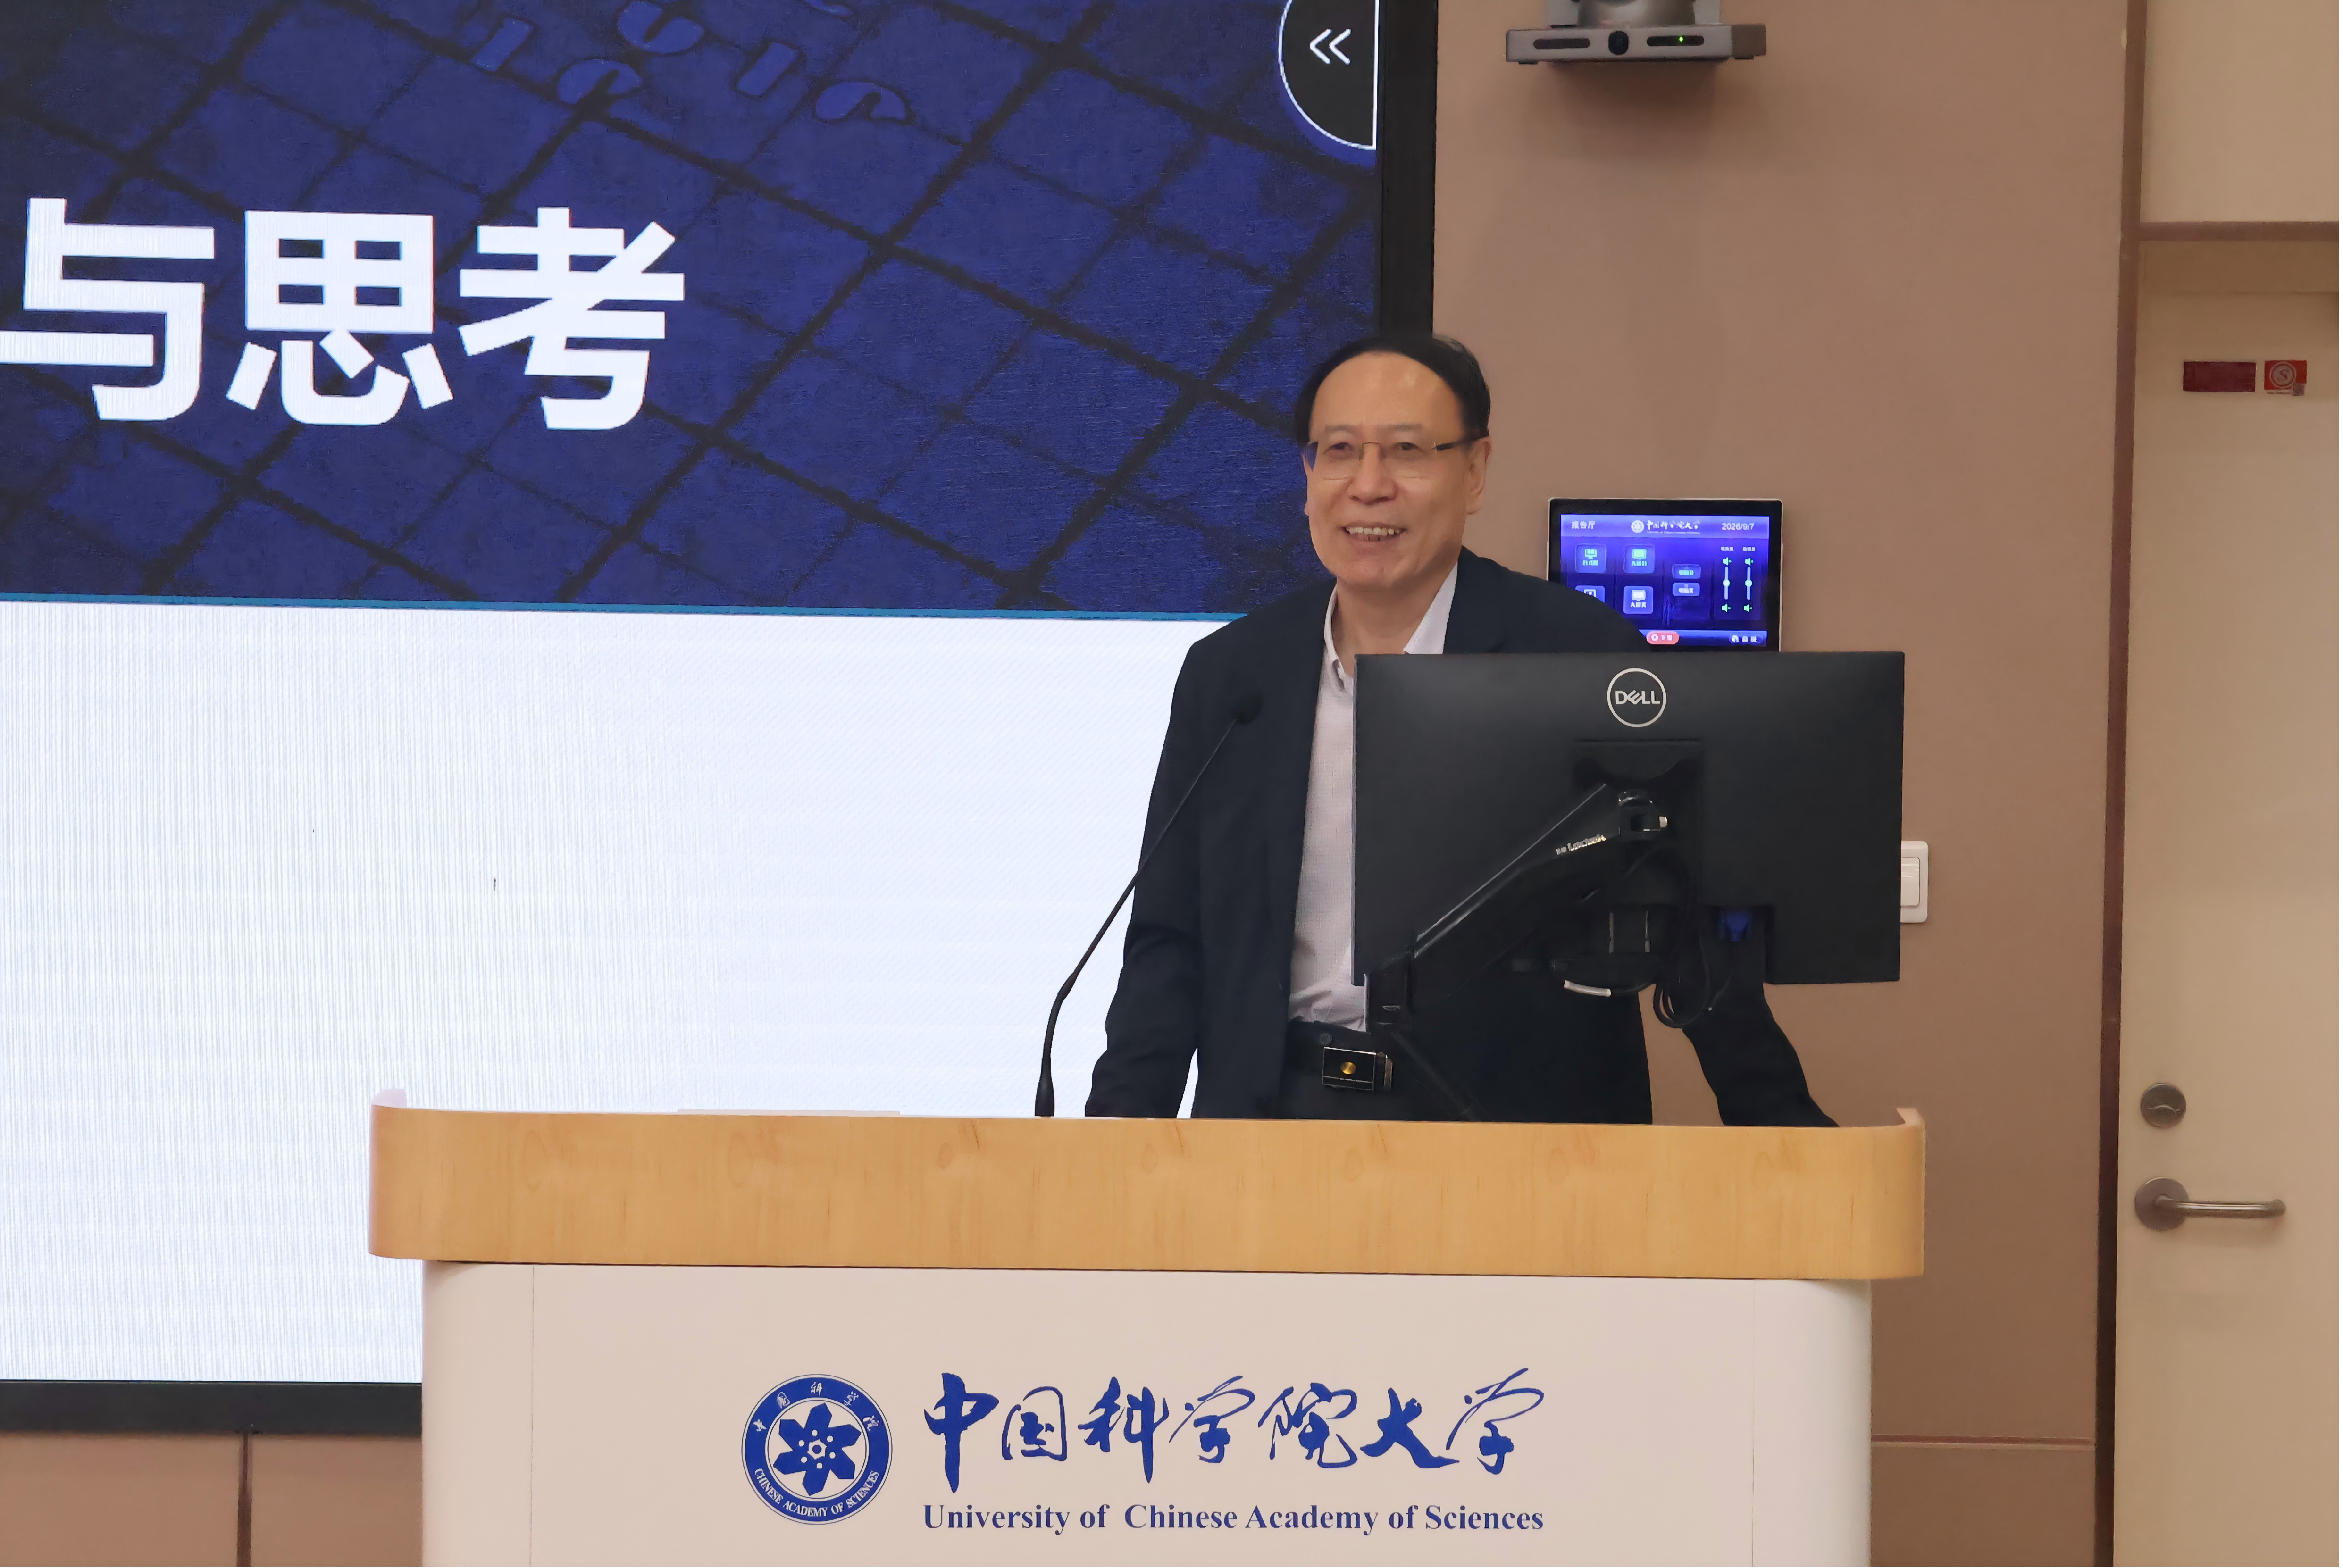
冯登国院士讲学院第一课
本次活动由密码学院荆继武院长主持,学院全体教职工、全体研究生导师、高年级在校学生及2026级新生共同参加。
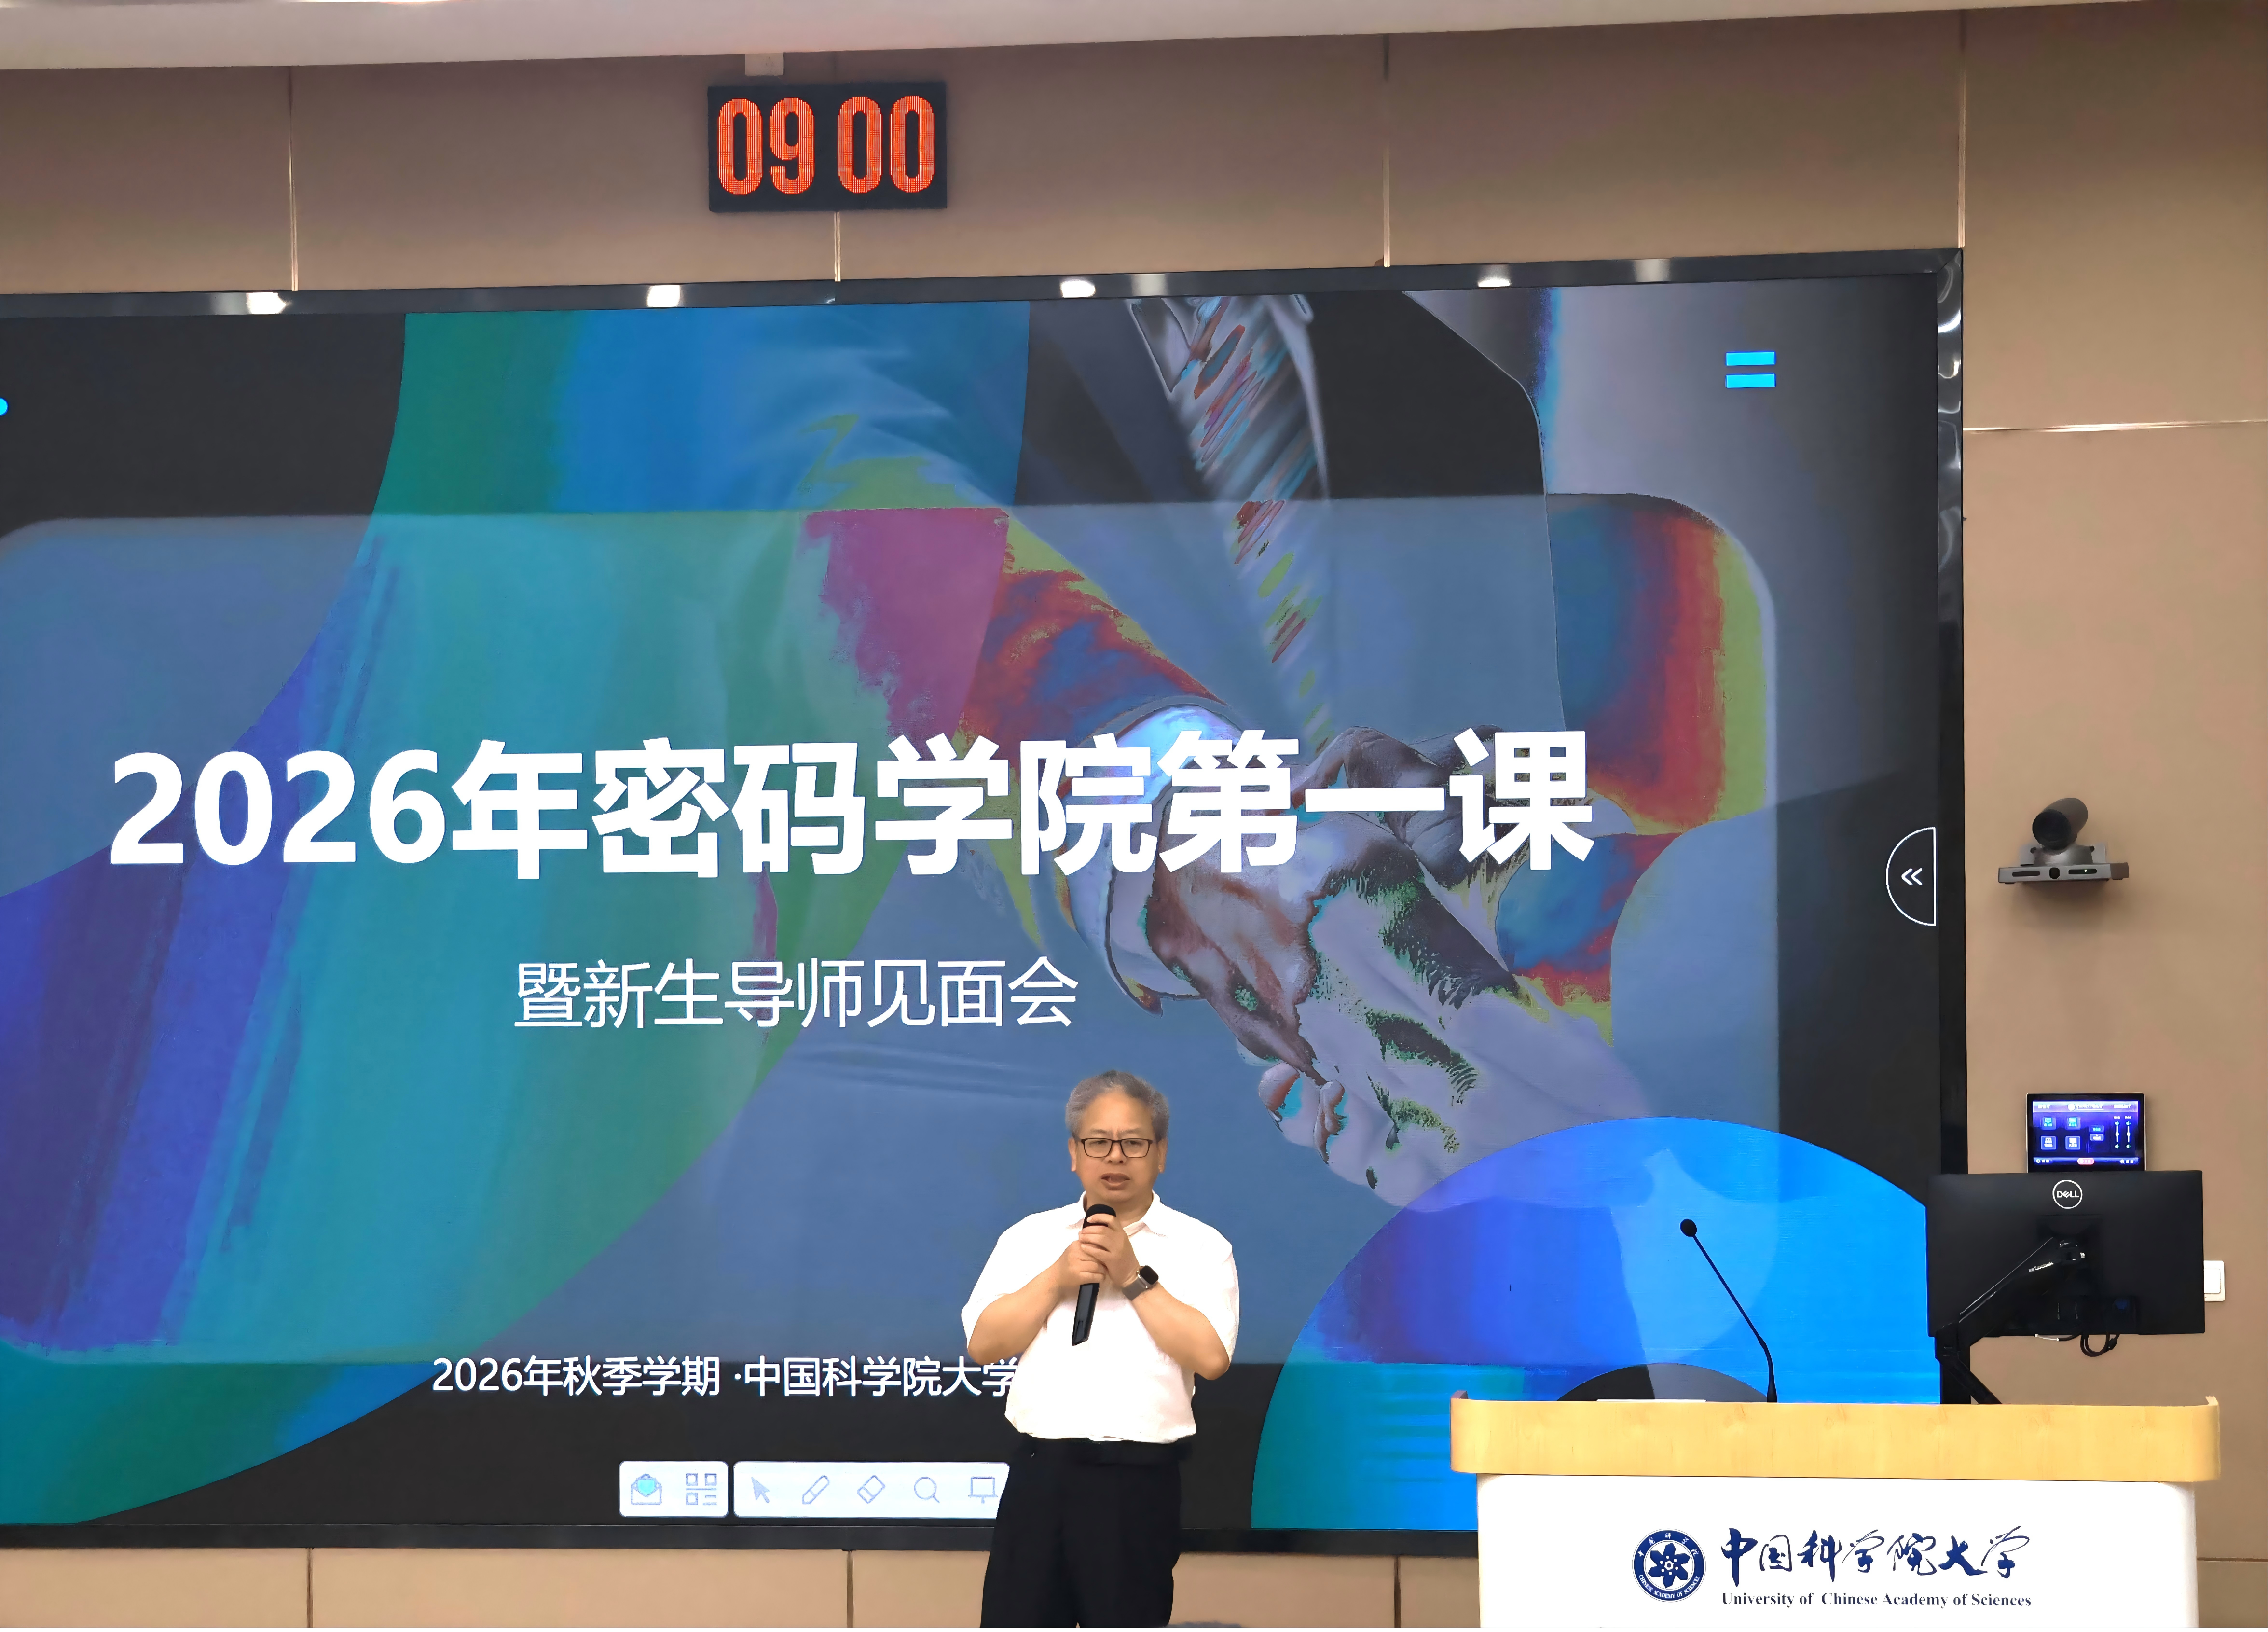
荆继武院长主持活动
第一课结束后,胡佳老师对研究生培养方案进行了系统解读,寇春静老师则详细介绍了学院奖助学金政策体系及资助额度。随后,参会导师与新生分组开展见面交流。
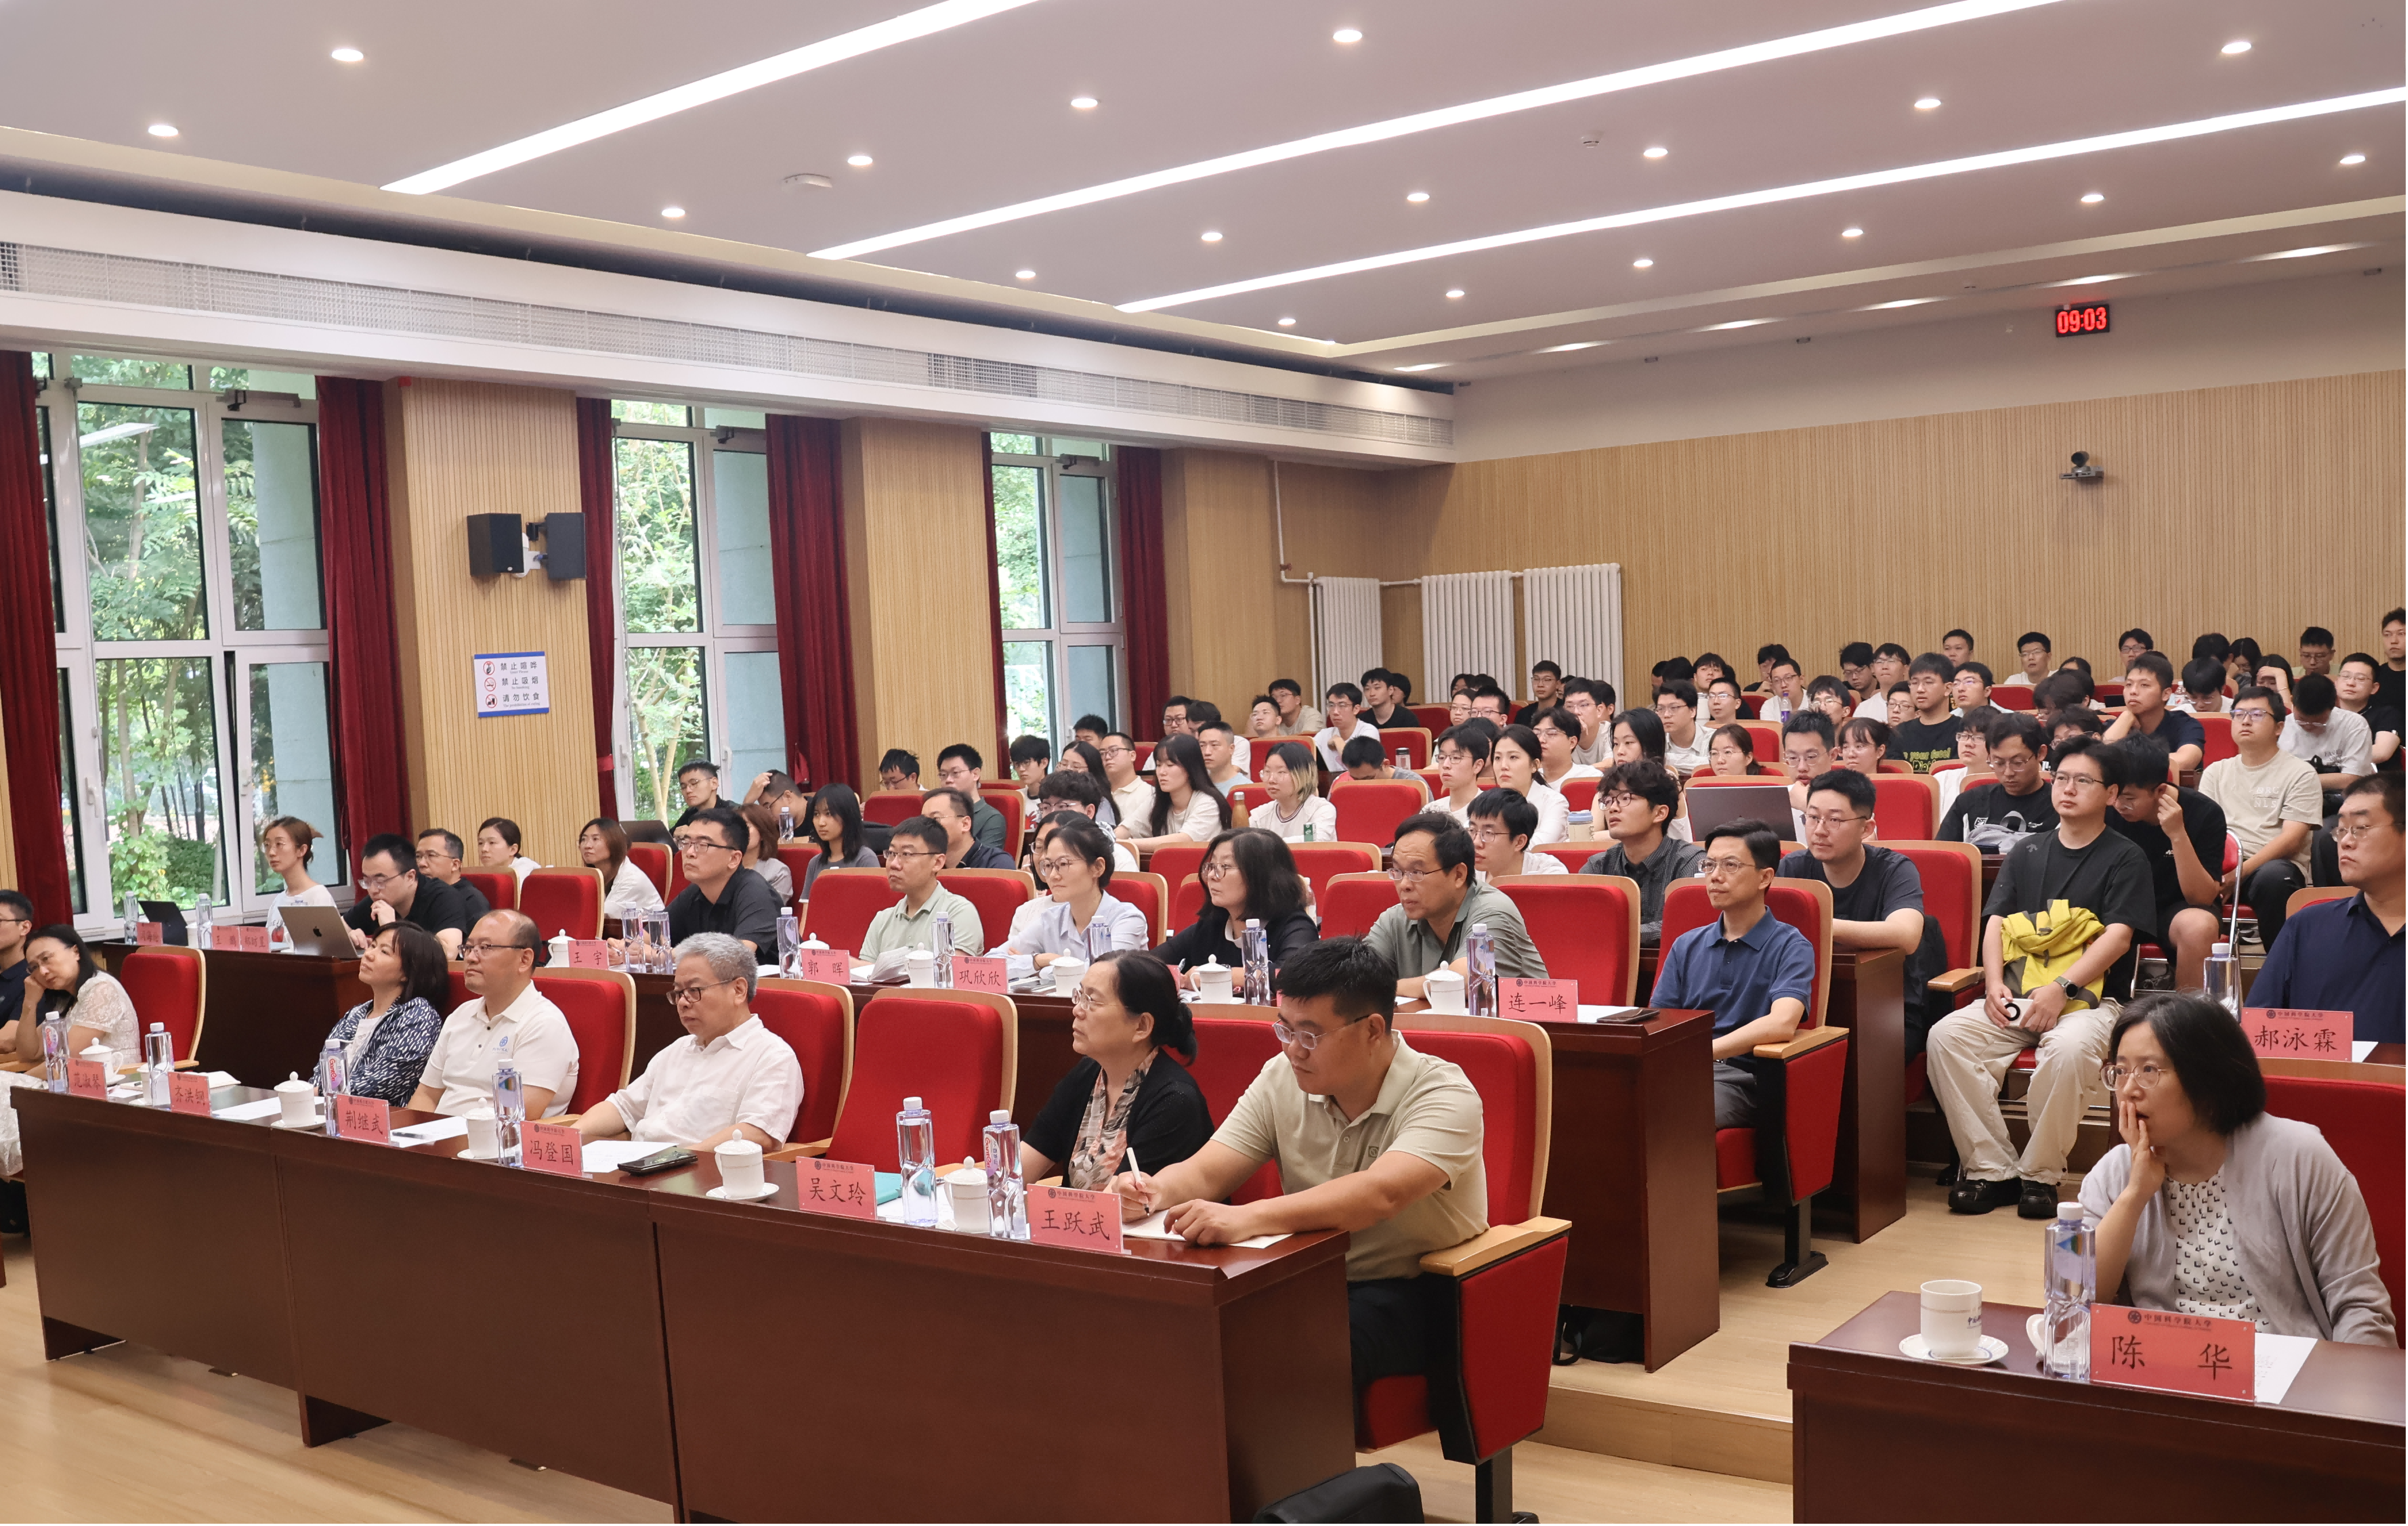
活动现场照片
2026年新春佳节来临之际,国科大党委常委、副校长牛晓莉与工会/教代会办公室主任李春楠一行专程来到密码学院,亲切看望慰问寒假期间依然坚守岗位的教职工,代表学校送上诚挚的新春祝福。
走访期间,校领导一行向学院教职工赠送了精心准备的手写春联、福字以及新春年货礼盒,将浓浓的节日气氛与暖意带到工作一线。“我们代表学校来看望大家!”“给大家拜年了,祝大家新年快乐!”牛晓莉副校长与在场教职工亲切交流,并认真听取了荆继武院长关于密码学院当前推进的重大专项、国家级示范密码学院建设等重点工作的汇报。
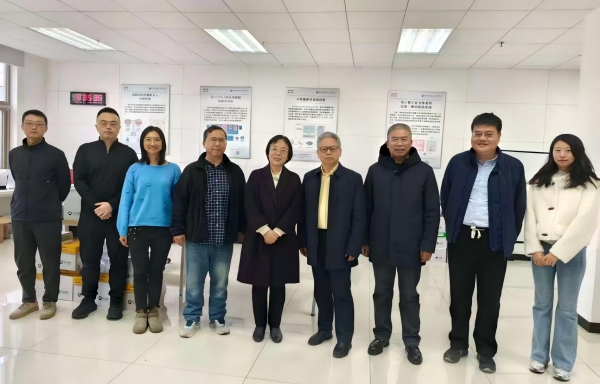
合影
校领导和工会的关怀令学院在岗教职工倍感温暖、深受鼓舞。大家共同将寓意吉祥的春联张贴在办公室门前,现场洋溢着喜庆祥和的氛围。教职工们纷纷表示,衷心感谢学校的牵挂与慰问,定将牢记使命、恪尽职守,在新的一年中以更加饱满的热情和扎实的行动,全力完成好国家与学校赋予的各项任务。
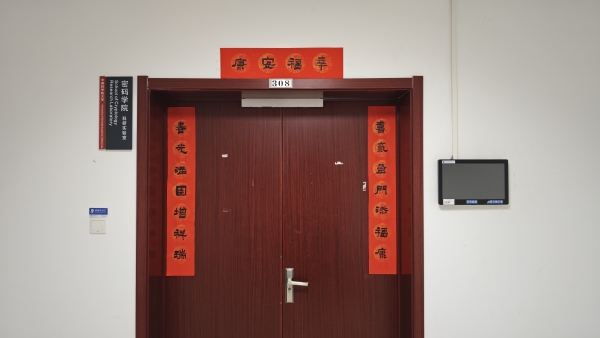
张贴春联